PLATFORM

One governed core, three projects

The Platform is the shared machinery beneath KRNL CLI, KRNL Harness, and KRNL OS: identity, memory, authority, execution, events, and a verifiable record of consequential work

Karnelian's connected agent architecture from soul to persistent memory
COMMON ARCHITECTURE

Interfaces change, authority does not

A terminal command, a desktop request, and a future operating-system service all enter the same explicit sequence

01

Intent

A person or trusted interface creates durable work

02

Context

Identity, session, memories, and relevant skills shape the request

03

Authority

Policy grants declared capabilities and pauses sensitive actions

04

Execution

A bounded worker performs the approved operation

05

Record

Events and ledger entries preserve what happened and why

Karnelian's connected agent architecture from soul to persistent memory
SECURITY + APPROVALS

Autonomy with visible borders

Capabilities are denied by default. Sensitive operations wait for a person, execution stays inside specialist runtimes, and safe mode can narrow authority across the system

Explore security
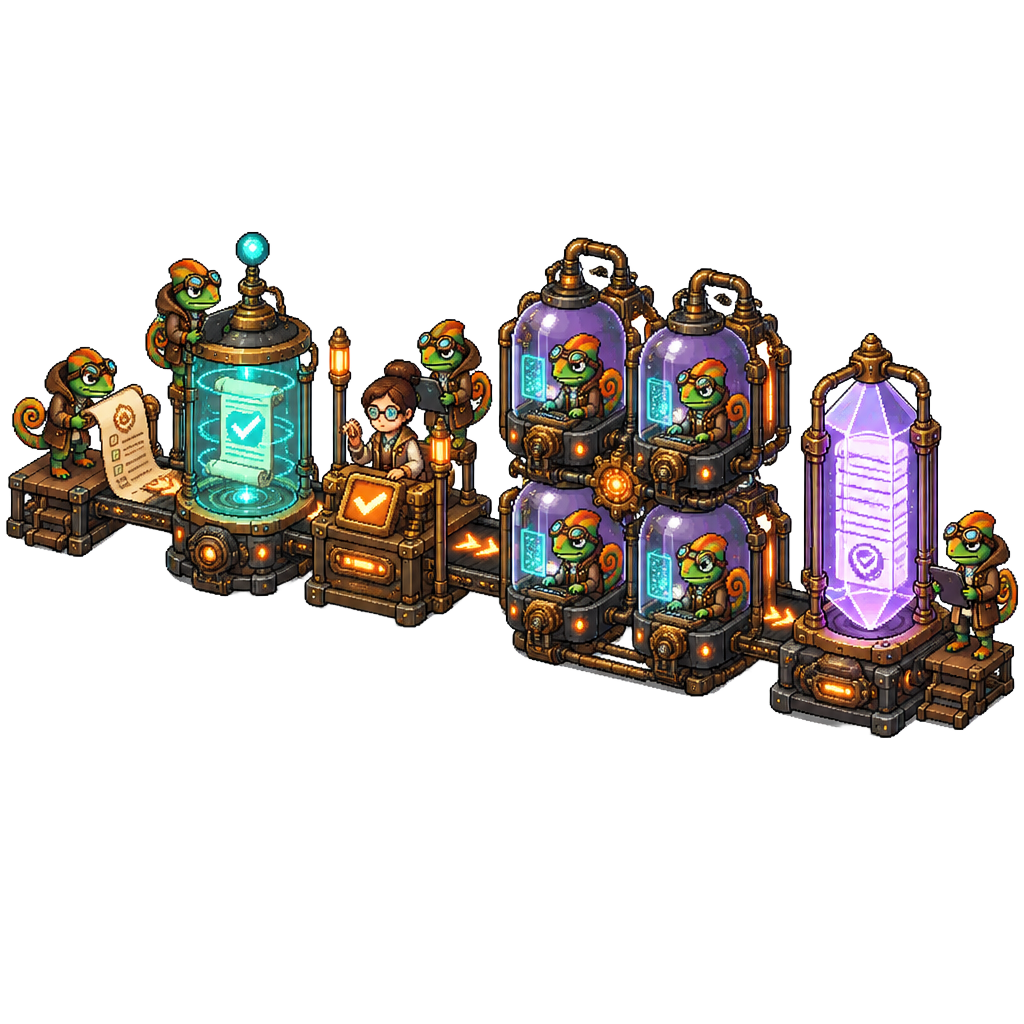
A governed task moving through approval, isolated workers, and an audit ledger
MEMORY + LEDGER

Remember usefully, record honestly

Semantic retrieval and reviewed Elixirs provide relevant context, while BLAKE3-linked ledger events make privileged history verifiable rather than merely narrated

Explore architecture
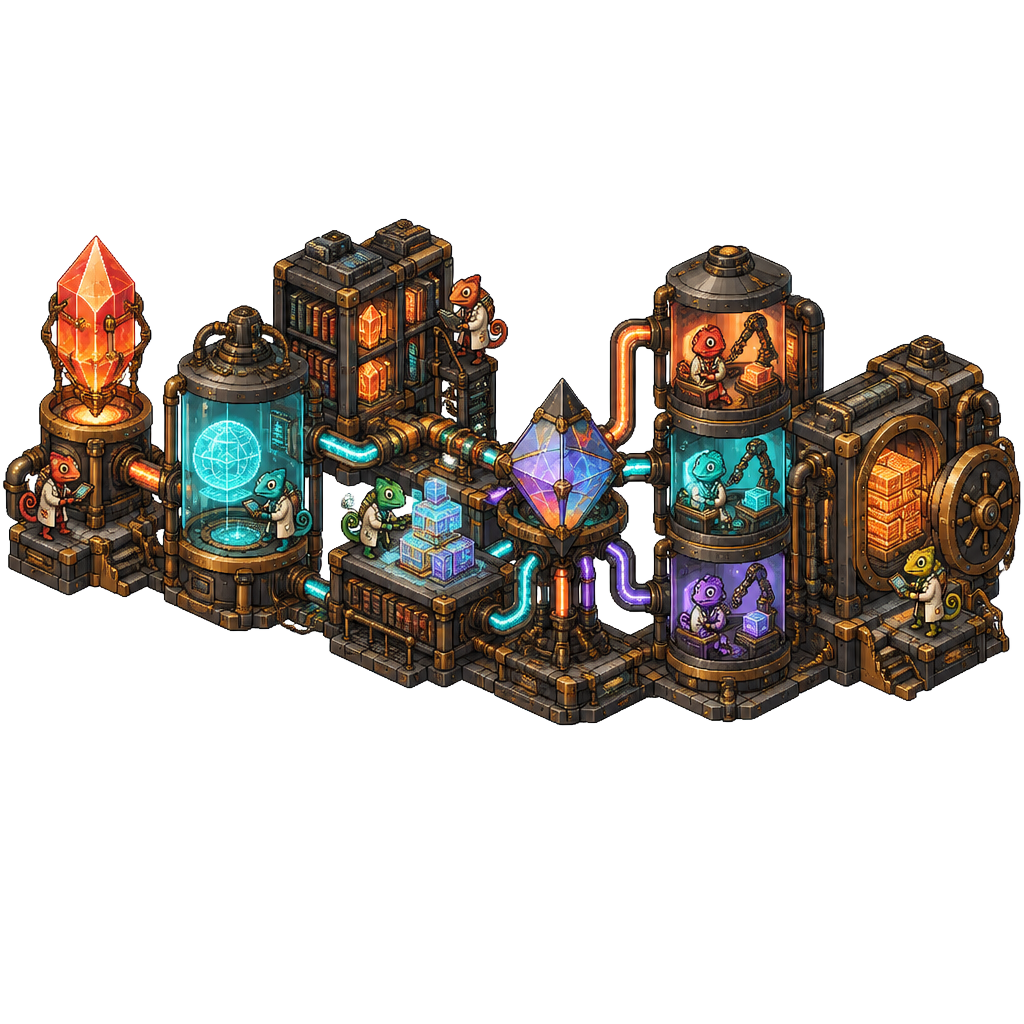
Mantra, heartbeat, and workflow-loop machinery operated by chameleons
SKILLS + WORKERS

Specialists enter through contracts

Skill manifests state required runtimes, resources, and capabilities so each agent receives only the authority its work requires

01

Declare

Name inputs, runtime, resources, and authority

02

Discover

Expose active capabilities through the Skill Book

03

Approve

Resolve access and request review where needed

04

Dispatch

Run work in an isolated specialist runtime

Lian dispatching work to isolated specialist runtimes
MAGIC RESEARCH

Randomness with provenance

The Mixed Authenticated Quantum Intelligence Core explores provider-aware entropy through Quantinuum H2, Qiskit sampling, and a secure operating-system CSPRNG fallback

EXPERIMENTAL

A research layer, not a cryptographic shortcut

MAGIC can vary mantra selection, provide ledger salts, and support quantum-category skills while preserving provider provenance

  • Eighteen mantra categories
  • A 555,555 millisecond heartbeat
  • Authenticated entropy provider selection
  • Post-quantum signatures remain future work
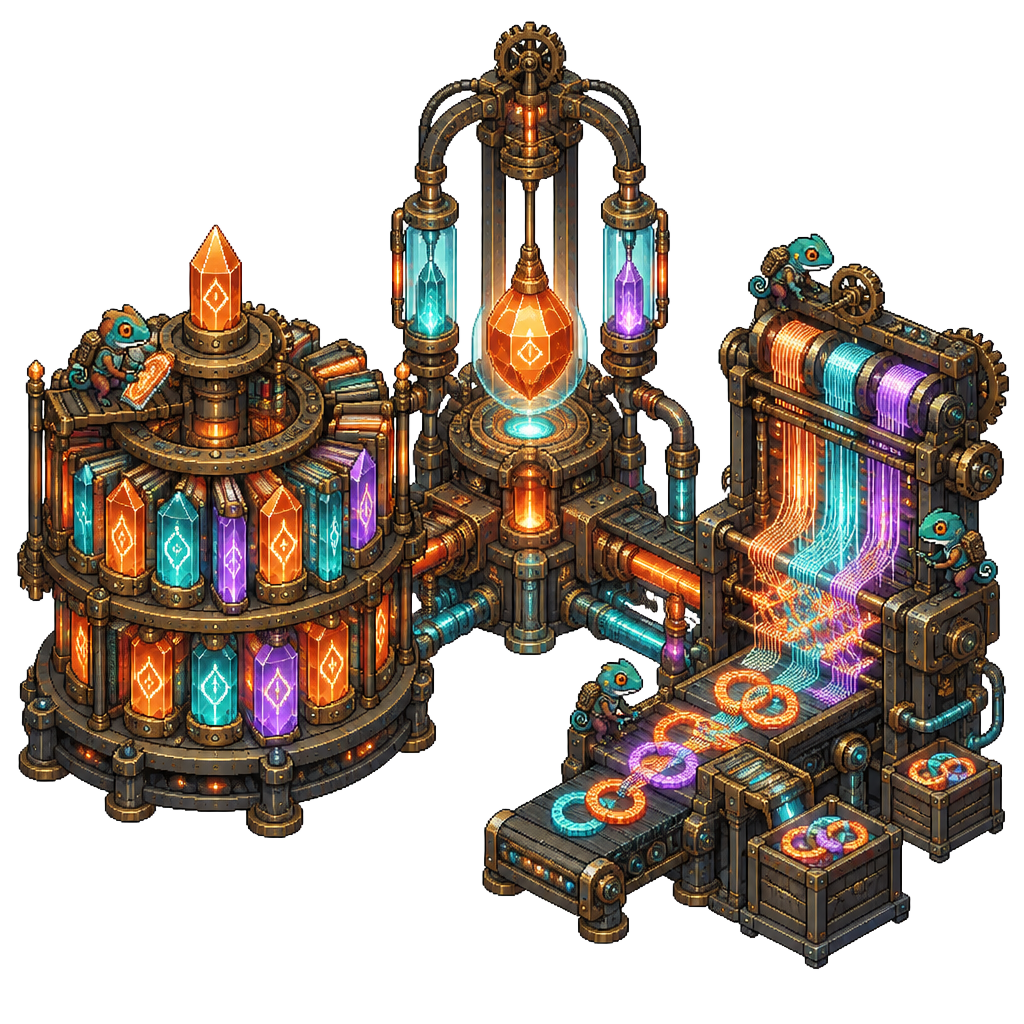
A chameleon scientist operating the MAGIC quantum research workbench
DEVELOPER SURFACE

Inspect, extend, and adapt the system

The open-source stack exposes its service boundaries rather than hiding them behind one assistant interface

RUST ORCHESTRATOR

Axum, Tokio, and SQLx coordinate sessions, tasks, events, scheduling, and persistence

REST + WEBSOCKETS

The /v1 control plane and /v1/events/ws connect interfaces to the same live system

EXTENSIBLE WORKERS

Build bounded skills in the runtime suited to the task without bypassing policy

ENTERPRISE FORKS

Adapt the open project into a company-wide assistant while retaining explicit governance

SOURCE-GROUNDED DOCS

Search setup, architecture, security, API, MAGIC, deployment, and troubleshooting guides

PUBLIC CONTRIBUTION

Inspect current boundaries and contribute without confusing ambition for shipped work