CAPABILITY SEALS
Agents and skills receive only the file, network, Git, shell, messaging, or deployment access they need.
Karnelian is built around least privilege: agents request specific powers, risky actions wait for approval, workers remain isolated, secrets stay encrypted, and privileged events enter a verifiable ledger.
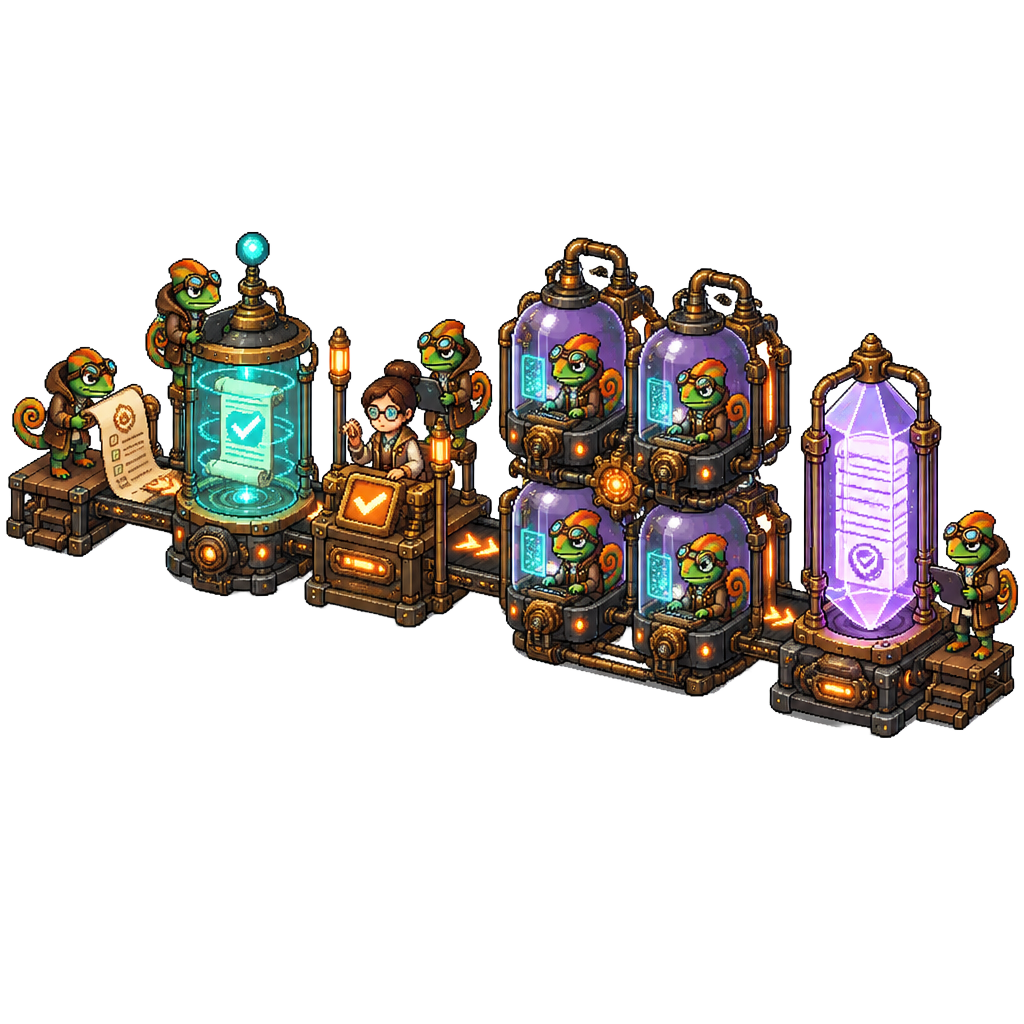
Authority is resolved before execution, not explained away afterward. The same chain applies whether a task starts from Lian, the CLI, or an API.
A skill manifest states its runtime, resources, and required capabilities.
Deny-by-default policy compares the request with granted authority.
Sensitive actions enter a human approval queue before they can proceed.
The selected worker executes inside its bounded runtime.
Signed authority and ledger events identify the request, decision, and outcome.
Agents and skills receive only the file, network, Git, shell, messaging, or deployment access they need.
Destructive or externally visible actions pause until an operator explicitly allows them.
Specialized runtimes contain execution and keep one failure from becoming system-wide authority.
An emergency control suspends risky capabilities and narrows the system to controlled operations.
Sensitive values use AES-256-GCM encryption at rest rather than entering prompts or logs as plain text.
Ed25519 attestations establish who requested, approved, and executed sensitive work.
Ledger records are linked with BLAKE3 hashes and can receive MAGIC-sourced entropy salts. The chain supports verification, slices, and anchoring, but it uses classical cryptography today.